
Critical RCE Vulnerabilities in PHP Core
On October 21, 2026, the PHP development team issued emergency security updates addressing two critical zero-day vulnerabilities affecting millions of web servers and applications globally. Dubbed "php2shell" and rated with a CVSS score of 9.2, these vulnerabilities (CVE-2026-109618 and CVE-2026-109619) allow unauthenticated remote attackers to execute arbitrary code (RCE) with full administrative privileges on target servers.
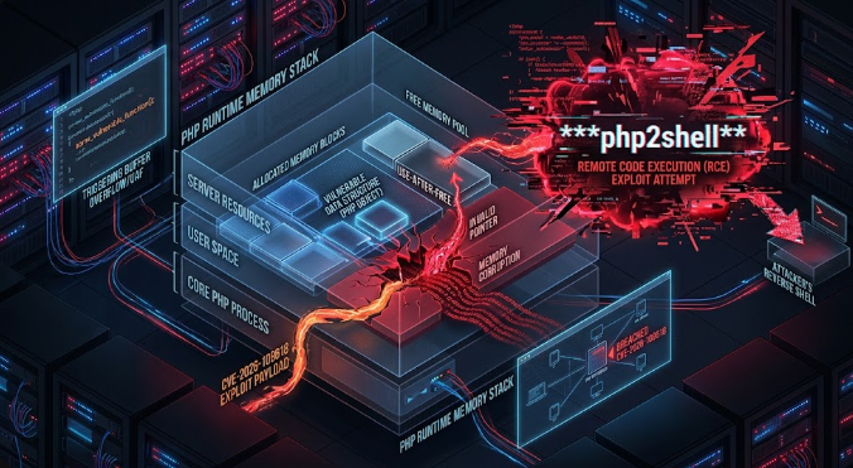
The flaws stem from memory corruption (Out of Memory handling) and stale global state management issues within the PHP core runtime. Attackers can send specially crafted HTTP requests to trigger memory corruption or Use-After-Free conditions even before any application code executes. Environments utilizing Apache mod_php, PHP-FPM, Nginx, as well as major CMS and e-commerce platforms, are at immediate high risk.
Some of the measures we need to take to protect against these types of critical runtime attacks are;
Update PHP versions: Upgrade to PHP 8.2.35, 8.3.36, 8.4.27, 8.5.12, or later versions containing the relevant security fixes.
Eliminate unsupported versions: Migrate from end-of-life PHP versions, such as PHP 7.4, 8.0, and 8.1, to supported releases.
Enable WAF protection: Monitor and block suspicious HTTP requests and abnormal file upload attempts.
Restrict access privileges: Run PHP services according to the Principle of Least Privilege.
Enhance security monitoring: Monitor web server logs and EDR alerts to detect suspicious activities.
For detailed information, you can contact our experts at info@zerosecond.ae.


Comments